
SOC 2 Criteria by Industry
Most companies approach SOC 2 as a checklist exercise. That’s a mistake.
SOC 2 is not just about passing an audit, it’s a strategic trust signal that directly impacts:
- Enterprise deal velocity
- Buyer confidence
- Risk posture
- Market positioning
And here’s the critical insight: Not all SOC 2 criteria matter equally for every industry.
The companies that win don’t just “get SOC 2”—they prioritize the right Trust Services Criteria based on what their customers actually evaluate.
Why Industry Alignment Matters
SOC 2 includes five Trust Services Criteria:
- Security (mandatory)
- Availability
- Processing Integrity
- Confidentiality
- Privacy
While security is required, the rest are selective levers.
Choosing the right combination determines whether your SOC 2 report:
- Accelerates deals
- Or becomes shelfware
Fintech & Payments: Trust = Accuracy + Security
Priority Criteria
- Security
- Processing Integrity ⭐ critical
- Confidentiality
- Availability
What Buyers Care About
Fintech buyers are not just evaluating whether your system is secure—they are asking:
- Are transactions accurate and tamper-proof?
- Can your system handle high-volume, real-time processing?
- Is sensitive financial data fully protected?
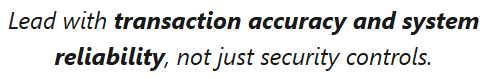
Even a small error in processing integrity can mean financial loss, compliance exposure, or fraud risk.
Strategic Positioning
If you're selling into fintech:
SaaS (B2B Platforms): Trust = Uptime + Reliability
Priority Criteria
- Security
- Availability ⭐ critical
- Confidentiality
What Buyers Care About
Enterprise SaaS buyers evaluate:
- Uptime guarantees (SLAs)
- System resilience under load
- Data protection mechanisms
Downtime directly impacts customer operations. Even short outages can break trust.
Strategic Positioning
Your SOC 2 narrative should emphasize:
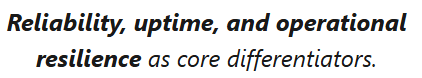
Healthcare / HealthTech: Trust = Data Sensitivity + Privacy
Priority Criteria
- Security
- Privacy ⭐ critical
- Confidentiality
What Buyers Care About
Healthcare organizations operate under strict expectations around:
- Patient data protection (PHI)
- Privacy controls and consent handling
- Secure data sharing between systems
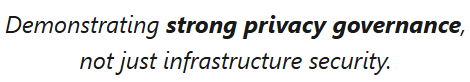
This is not just technical—it’s deeply tied to regulatory and ethical risk.
Strategic Positioning
Winning in healthcare requires:
E-commerce / Retail Tech: Trust = Experience + Protection
Priority Criteria
- Security
- Privacy ⭐ critical
- Availability
What Buyers Care About
E-commerce platforms must balance:
- Customer data protection
- Seamless user experience
- High availability during peak traffic
A failure in any of these areas impacts both revenue and brand trust.
Strategic Positioning
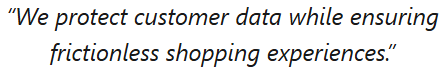
Your message should be:
Manufacturing / Supply Chain: Trust = Continuity + IP Protection
Priority Criteria
- Security
- Availability
- Confidentiality
What Buyers Care About
In manufacturing and supply chains:
- Downtime disrupts physical operations
- Data includes intellectual property and supplier contracts
- Systems must remain consistently operational
Strategic Positioning
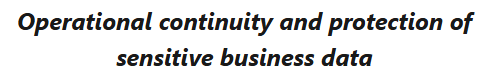
SOC 2 should highlight:
Cybersecurity & IT Services: Trust = Full Coverage
Priority Criteria
- All 5 Criteria ⭐ expected
What Buyers Care About
If you are a security or IT provider:
- You are not just compliant—you are a trust authority
- Clients expect comprehensive assurance across all domains
Anything less creates credibility gaps.
Strategic Positioning
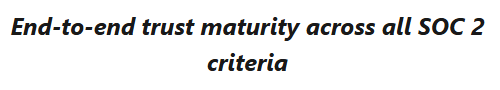
You need to demonstrate the following:
EdTech: Trust = Safety + Accessibility
Priority Criteria
- Security
- Privacy
- Availability
What Buyers Care About
EdTech platforms must ensure:
- Student data protection
- Uninterrupted learning experiences
- Safe digital environments
Especially critical for live classes and remote learning.
Strategic Positioning
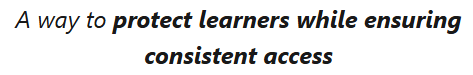
Position SOC 2 as:
The Strategic Mistake Most Companies Make
Many organizations either:
- Choose too few criteria → lose enterprise deals
- Choose too many criteria → over-invest and slow down
SOC 2 becomes expensive—but not effective.
A Smarter Approach to SOC 2
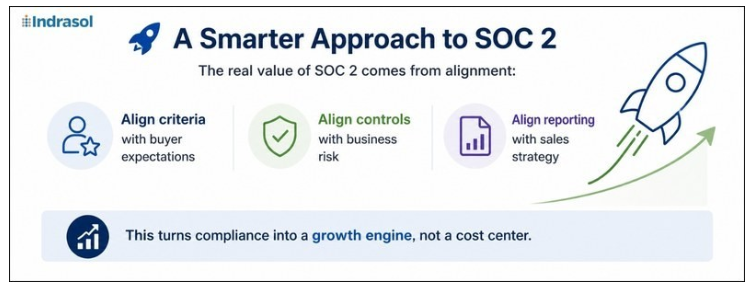
The real value of SOC 2 comes from alignment:
- Align criteria with buyer expectations
- Align controls with business risk
- Align reporting with sales strategy
This turns compliance into a growth engine, not a cost center.
Final Takeaway
SOC 2 is not one-size-fits-all.
The companies that extract real value from it are the ones that ask:
Indrasol Perspective
At Indrasol, the focus is not just on helping companies become compliant.
It’s on helping them:
- Choose the right criteria
- Avoid unnecessary complexity
- Use SOC 2 as a tool to win trust and close deals faster
About the Author
Satish Govindappa
Satish Govindappa is an Visionary technology leader with 15+ years of experience spearheading AI/ML transformations across complex enterprise environments. Proven ability to align AI initiatives with business goals, lead global cross-functional teams, and deliver scalable, cloud-native solutions using LLMs, predictive analytics, and anomaly detection. Skilled in building AI Centers of Excellence, developing architecture standards, and ensuring responsible AI adoption across the organization. Championed a multi-million dollar Generative AI program at Synopsys, leading the development and deployment of custom large language models (LLMs) to strengthen compliance, accelerate product innovation, and streamline critical operational workflows. Facilitated architectural design sessions with IT architects and engineering leaders to build scalable, cloud-native AI infrastructure, enabling smooth integration with Synopsys and ICE Mortgage Technology’s distributed enterprise systems. Orchestrated the creation of enterprise-wide AI architecture standards, standardizing the deployment of predictive analytics, real-time anomaly detection, and large language model (LLM) solutions across diverse business units. Directed cross-functional teams of global professionals, uniting IT, operations, and business units to drive successful adoption of Generative AI applications. Experienced Generative AI Security Architect with solid background in LLM security, AI threat modeling, and machine learning to protect AI systems from prompt injection, model poisoning, and data leakage. Proficient in Cloud AI security (AWS, Azure, GCP), MLOps security, and Zero-trust AI architectures. Securing AI applications for Fortune 500 enterprises, startups, and government agencies across the US, EU, and APAC. Committed to ensuring AI compliance (SOC 2, NIST AI RMF, GDPR, ISO 27001) and enterprise AI risk management Expert in securing Generative AI and Large Language Models (LLMs) against emerging threats such as prompt injection, model poisoning, and adversarial machine learning attacks. A J2EE Developer turned Application Security Professional with unique ability to understand both the worlds better (Development and Security). Working experience in top companies like Fidelity Investments, TD Ameritrade, DTCC, MindTree, Honeywell and AOL. Specialties: GenAI Security, LLM security, Threat Modeling, Secure Code Review, Web Penetration Testing, Server Audits, Security Training, Security Automation
View Satish Govindappa's profile