Audit-ready, without the spreadsheets.
SecureTrack is the compliance platform for SOC 2 and CMMC. Controls, evidence, policies, people, vendors and risks live in one workspace, and your audit reports come straight from live data.
Request early accessIllustrative data. Each unmet practice deducts 1, 3 or 5 points from 110, as in the DoD Assessment Methodology.
Compliance shouldn't live in ten places.
Spreadsheets for controls, shared folders for evidence, email threads for sign-offs and a Word file for the SSP. SecureTrack replaces the patchwork with one single source of truth for your whole team.
Every control, piece of evidence, policy, signature, vendor and risk in one place, and every report generated from the same live data.
Two frameworks live today.
Ready for your C3PAO, and for SPRS.
Built on the official DoD control IDs, with your SPRS score recalculated live as each practice changes status.
- Level 1: self-assess the 15 practices, then the annual affirmation is signed by your senior official through a secure link
- Level 2: the 110 NIST SP 800-171 practices, scored live as SPRS
- SPRS scoring based on the DoD Assessment Methodology: start at 110, deduct 1, 3 or 5 points per unmet practice
- Vendors handling CUI without FedRAMP authorization flagged as blockers
Everything your audit asks for, connected.
Controls, evidence, tasks, vendors and risks, all connected, so a change in one place shows up everywhere it matters.
Live readiness, at a glance
Readiness rings for each level, your current SPRS score, readiness by NIST 800-171 family and the top gaps to close this quarter.
- Readiness by domain
- Highest-weight gaps first
- Recent activity and upcoming deadlines
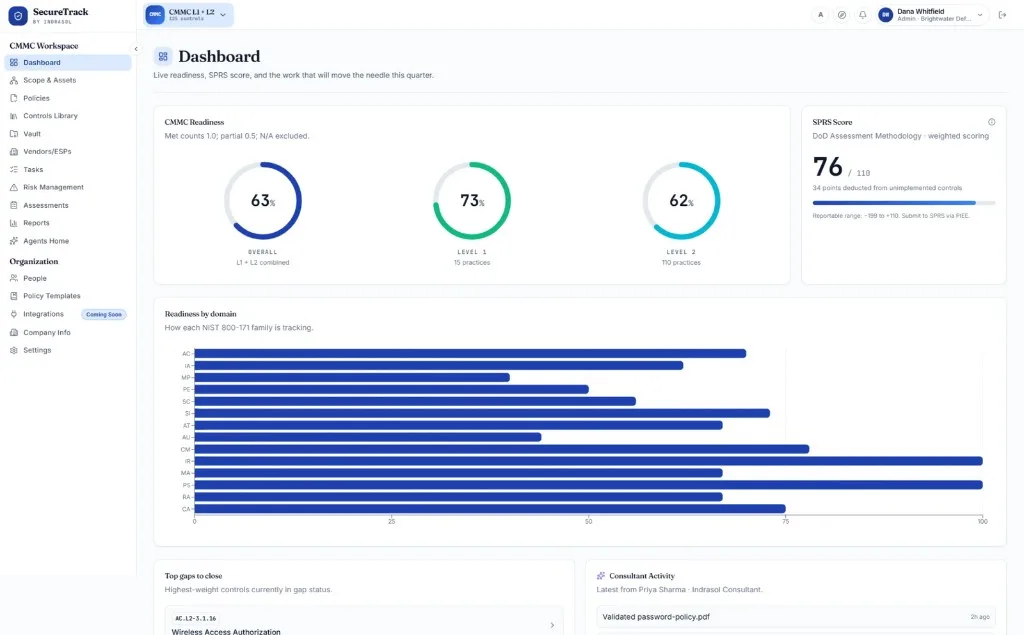
Screens shown with demo data.
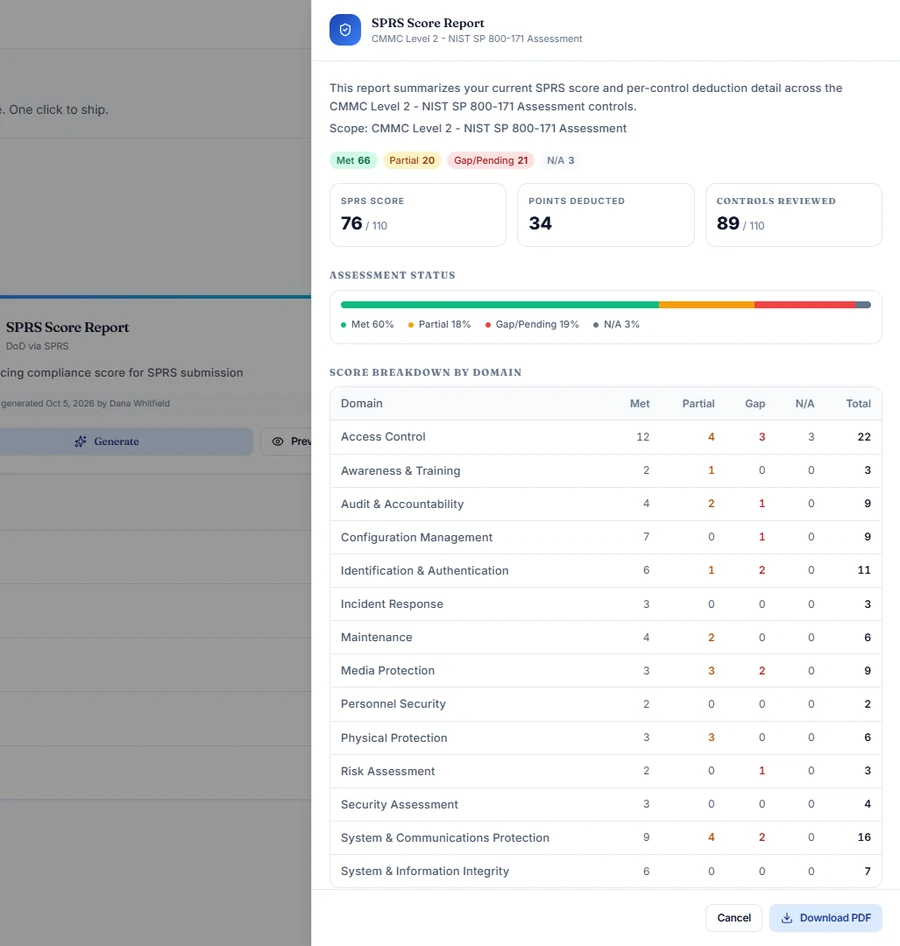
One click from live data to audit deliverables.
Reports are generated from your live data, so you're never rebuilding documents the week before an assessment.
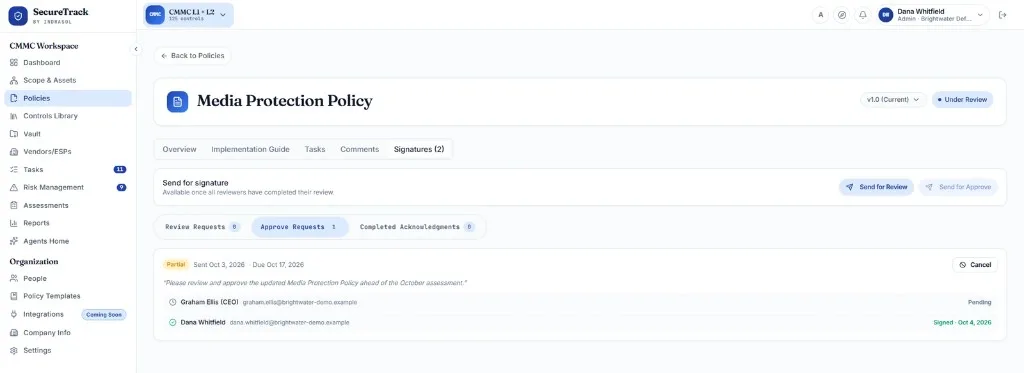
Approvals without another login.
Send a policy for review, approval or acknowledgment. Your signer opens a secure link, reads a locked snapshot and signs. The same flow carries the CMMC annual affirmation.
- 1SendChoose review, approve or acknowledge, and set a due date.
- 2Secure linkThe signer gets a one-time link by email. No login.
- 3Read the snapshotThey see the policy exactly as it was when sent, so later edits can't change it.
- 4Sign or declineWith a drawn signature, recording IP address and browser.
- 5Done, or expiredThe link closes at the due date, or can be cancelled.
The right access for everyone, auditors included.
Give your assessor read-only access to exactly one framework, with an end date, instead of emailing folders back and forth.
Admin
Usually the compliance lead. Full control of the workspace, people, settings and integrations.
Contributor
Control owners in IT, HR and facilities. Update controls, upload evidence, work tasks and reports.
Viewer
Read-only access to compliance data, plus the AI assistant.
Auditor
Read-only access for assessors, scoped to one framework and optionally set to expire. Records their own findings.
Executive signer
Your CEO or senior official signs policy approvals and affirmations through a secure link. No account needed.
Less drafting, more deciding.
Draft policies with AI
Give a short brief and AI drafts the policy using your company profile as context. Review it, edit it, send it for sign-off.
SSP control summaries
AI writes a summary for each control in your System Security Plan, and only regenerates it when that control's inputs change.
CMMC Q&A assistant
Ask CMMC questions and get answers grounded in CMMC and NIST material, with citations.
Your evidence, locked to your organization.
- Encryption
- Evidence, reports, policies and vendor documents encrypted with AES-256-GCM before they're stored
- Your own key
- Each organization has its own 256-bit key, held in Azure Key Vault. One customer's key can't open another's files
- Isolation
- Row-level security separates each organization's data in the database
- Hosting
- Microsoft Azure, in the United States
- Sign-in
- Passwordless, by one-time email code
More frameworks, more connections.
Built by a security company that runs audits.
SecureTrack reflects how assessments actually work. Want Indrasol's consultants alongside the platform? Our compliance teams run SOC 2 and CMMC readiness end to end.
How do I get access?
SecureTrack is in early access. Request access through our team: Indrasol reviews each request and gets in touch. Prefer to see it first? Book a demo.
Does it support SOC 2 Type I and Type II?
Yes. Both are readiness modes of the same SOC 2 framework, with a Readiness Report for each.
Is the SPRS score the official DoD score?
Scoring is based on the DoD Assessment Methodology for NIST SP 800-171: it starts at 110 and deducts 1, 3 or 5 points per unmet practice. CMMC Level 1 is a self-assessment and affirmation, so it has no SPRS score.
Is evidence collected automatically?
Not yet. Today you upload evidence to the vault and link it to controls. Connectors that pull evidence from tools like AWS, Microsoft 365, Okta and GitHub are coming soon.
Can our auditor review evidence directly?
Yes. Invite them with the Auditor role: read-only, limited to one framework, and optionally set to expire at the end of the engagement.
Where does AI come in?
AI drafts policies from a short brief using your company profile, and writes control summaries for your System Security Plan. A CMMC Q&A assistant with cited answers is in early access.
How is our data protected?
Evidence, reports and policies are encrypted with AES-256-GCM using a key unique to your organization, and database rows are separated per organization. Sign-in is passwordless, by one-time email code.
Walk into your next audit ready.
Book a demo and our team will walk you through SecureTrack with your own framework.