
AI Security Risk Management: The 5-Step Cycle Every Enterprise Needs
An AI system can be secure when it is deployed and become a significant security risk months later.
The model may not have changed.
But the data may have changed. The integrations may have changed. The permissions may have expanded. New users may be accessing it. New vulnerabilities may have emerged. Attack techniques may have evolved.
That is why AI security cannot be treated as a point-in-time assessment.
For enterprises adopting generative AI, large language models, AI agents, machine learning applications, and AI-powered business processes, AI security** risk management needs to operate as a continuous cycle.**
A practical model is:
Identify → Assess → Implement Controls → Monitor → Review & Update → Repeat
The objective isn't simply to find AI vulnerabilities. The objective is to continuously understand what can go wrong, how much it matters, whether controls are working, and what has changed.
WHAT IS AI SECURITY RISK MANAGEMENT?
AI security risk management is the continuous process of identifying, assessing, mitigating, monitoring, and updating risks associated with AI systems, models, data, applications, users, integrations, and vendors.
Traditional security programs often rely on periodic assessments. AI environments make that approach increasingly difficult.
An AI application might gain access to a new data source. An agent might receive additional permissions. A third-party model might be updated. Employees might begin using an AI tool that was never formally approved.
The risk environment changes. The security program needs to change with it. This is where a continuous AI risk management framework becomes important.
THE AI SECURITY RISK MANAGEMENT CYCLE
The five stages are:
- Identify Risks
- Assess Impact
- Implement Controls
- Monitor Performance
- Review & Update
Back to Identify Risks
The last stage is deliberately connected back to the first. Because AI security isn't finished when a control is implemented.
1. Identify AI Security Risks
You cannot manage an AI risk you don't know exists. The first step is building visibility across the organization's AI environment.
This goes beyond identifying approved AI applications. Security teams need to understand the entire AI ecosystem, including:
- AI and LLM applications
- Foundation models
- AI agents
- APIs
- Data sources
- Enterprise integrations
- AI-generated code
- Cloud infrastructure
- Third-party AI vendors
- Model providers
- Users and administrators
- Access permissions
- Shadow AI
Consider an AI agent connected to an enterprise CRM. The model itself may not represent the biggest risk.
The bigger question could be: What can the agent do with the access it has?
- Can it read customer records?
- Can it modify data?
- Can it send emails?
- Can it execute transactions?
- Can a prompt injection manipulate it into performing an unauthorized action?
The risk exists at the intersection of model + data + tools + permissions + business process.
Questions security teams should ask
- What AI systems are actually being used?
- Which applications are business-critical?
- What data can each AI system access?
- Which systems are connected to AI agents?
- What permissions have AI agents been granted?
- Which third-party models and vendors are involved?
- Where can sensitive or regulated information enter AI workflows?
- Are employees using unapproved AI tools?
Potential risks can include prompt injection, sensitive data leakage, model manipulation, data poisoning, insecure APIs, excessive permissions, supply-chain vulnerabilities, and unauthorized access to enterprise data.
The first objective is visibility. Without it, AI security becomes guesswork.
2. Assess the Impact
Identifying a vulnerability is only the beginning. The next question is: How much does this risk actually matter to the business?
A technical vulnerability with a high severity score doesn't automatically represent the highest business risk.
Consider two AI applications with the same prompt-injection vulnerability. One is an internal productivity chatbot with access to public information. The other is an AI agent connected to financial systems and sensitive customer data.
The technical vulnerability may be similar. The business impact is not.
AI risk assessment should consider factors such as:
- Likelihood of exploitation
- Business criticality
- Data sensitivity
- Regulatory exposure
- Financial impact
- Operational disruption
- Customer impact
- Intellectual property exposure
- Reputational damage
- Attack paths
- Existing compensating controls
This distinction is critical. Security teams shouldn't simply ask:
They should also ask:
That is the difference between vulnerability management and meaningful AI risk management.
3. Implement the Right Controls
Once risks have been prioritized, organizations need to translate those risks into practical security controls.
There is no single control that makes an AI system secure. Effective enterprise AI security typically requires multiple layers.
Identity and access management
Apply least privilege to users, applications, APIs, and AI agents. An AI agent should have only the permissions necessary to perform its defined function.
Understand what data is entering AI systems and where that data goes.
Sensitive information should not automatically become available simply because an AI application can process it.
AI guardrails
Establish policies around acceptable inputs, outputs, actions, and data access.
Secure AI development
AI applications should be subjected to security testing throughout development and deployment—not only after production release.
Prompt and input validation
Organizations should consider protections against malicious instructions, prompt injection, and unexpected inputs.
Output monitoring
AI-generated outputs should be evaluated based on the risk of the application.
A marketing assistant and an AI system supporting a high-impact business decision should not necessarily have the same level of oversight.
API and integration security
Every connection between an AI system and another application creates another potential attack surface.
Human oversight
High-impact AI actions may require human approval rather than unrestricted autonomous execution.
Third-party risk management
Organizations also need to understand the security practices, data handling, model dependencies, and changes associated with external AI providers.
The objective isn't to implement the maximum number of controls. It is to implement** controls proportional to the risk.**
4. Monitor Performance
Implementing a security control does not mean the risk has disappeared. This is one of the most important differences between traditional compliance thinking and effective AI security.
- A policy can exist.
- A control can be implemented.
- A dashboard can show green.
And the organization can still be exposed. Continuous AI security monitoring should look at whether controls are actually working.
Security teams should monitor:
- AI interactions
- Model behavior
- Data access
- User activity
- Agent actions
- API activity
- Security events
- Policy violations
- Model changes
- Data-source changes
- New vulnerabilities
- Third-party changes
- Control effectiveness
For example, an AI agent may originally have access to three systems. Six months later, it might have access to eight.
- Was that change reviewed?
- Was the risk reassessed?
- Are the additional permissions still necessary?
- Has the agent started performing actions outside its original use case?
These are monitoring questions not merely configuration questions.
The important metric isn't “Do we have a control?” It is: “Is the control reducing risk?”
5. Review and Update
AI security programs cannot remain static while AI environments evolve. The final stage of the cycle is reviewing what has changed and updating the risk management strategy.
Triggers for reassessment can include:
- A new AI model
- A new AI agent
- A new integration
- A major model update
- A new data source
- A change in AI usage
- A new vulnerability
- A new attack technique
- A security incident
- A change in business processes
- A change in third-party providers
- Changes in applicable requirements
This creates an important feedback loop.
Monitor → Learn → Review → Update → Identify New Risks
That feedback loop is what turns AI security from a compliance exercise into an operational capability.
THE 5 QUESTIONS EVERY ENTERPRISE SHOULD ASK ABOUT AI SECURITY
Security and technology leaders can use five simple questions to evaluate their current AI security maturity:
1. What AI systems do we actually have?
If the organization cannot answer this confidently, visibility is the first priority.
2. What can those systems access?
Map models, applications, agents, APIs, data sources, and permissions.
3. What could go wrong?
Identify realistic attack scenarios and business consequences—not just theoretical vulnerabilities.
4. Are our controls actually reducing risk?
Measure control effectiveness instead of simply documenting control implementation.
5. What has changed since our last assessment?
This question is critical.
If the answer is “we don't know,” the organization may have a visibility and governance problem.
WHY AI SECURITY IS A BUSINESS ISSUE
AI security is often positioned as a technical challenge. It is much bigger than that. A significant AI security incident could affect:
Customer trust Customers expect organizations to protect their information regardless of whether the data is processed by a traditional application or an AI system.
Intellectual property Sensitive product information, source code, research, and proprietary knowledge can become exposed through poorly governed AI usage.
Regulatory and compliance obligations Organizations need to understand how AI systems interact with existing privacy, security, risk, and governance requirements.
Operational resilience An AI agent connected to critical systems can introduce new operational risks if it behaves unexpectedly or is compromised.
Enterprise sales Customers increasingly want to understand how vendors protect the AI systems processing their data.
AI adoption itself If security teams cannot establish reasonable controls, business leaders may hesitate to deploy AI at scale.
This is why AI security should enable AI adoption not simply restrict it.
The goal isn't to prevent organizations from using AI. The goal is to help them use AI securely, responsibly, and at scale.
THE BIGGER SHIFT: FROM AI SECURITY ASSESSMENT TO CONTINUOUS AI RISK MANAGEMENT
The traditional mindset is:
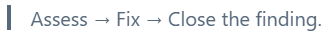
The AI security mindset needs to be:

That difference matters.
- AI environments are dynamic.
- Models change.
- Applications change.
- Data changes.
- Users change.
- Permissions change.
- Threats change.
- Business processes change.
Therefore, the risk changes. Knowing what AI systems exist is becoming as important as knowing what cloud assets exist.
And understanding the model alone isn't enough. Security teams need visibility into the entire AI system and its surrounding ecosystem.
FINAL TAKEAWAY
AI security should not be treated as a one-time assessment performed before deployment. It should operate as a continuous risk management cycle.
- Identify the risks.
- Assess their business impact.
- Implement appropriate controls.
- Monitor whether those controls work.
- Review what has changed and start the cycle again.
The organizations that build this discipline will be better positioned to scale AI without allowing security risk to scale at the same speed.
The goal isn't simply secure AI deployment. It's continuous secure AI adoption.
5 KEY TAKEAWAYS
- AI security is continuous. A point-in-time assessment cannot keep pace with changing models, data, permissions, applications, and threats.
- Visibility comes first. Organizations need to know what AI systems exist, what data they access, and what actions they can perform.
- Technical severity isn't business risk. AI risks should be prioritized according to their potential impact on customers, operations, data, revenue, and reputation.
- Controls need to be measured. Implementing a control is not the same as proving that it reduces risk.
- Review must feed back into identification. New models, integrations, vulnerabilities, usage patterns, and threats should continuously trigger reassessment.
FAQs
1. What is AI security risk management?
AI security risk management is the continuous process of identifying, assessing, mitigating, monitoring, and updating risks associated with AI systems, models, data, applications, users, integrations, and vendors.
2. What are the biggest AI security risks?
Common risks include prompt injection, sensitive data leakage, excessive AI permissions, insecure AI agents, model and data poisoning, insecure APIs, third-party AI risks, shadow AI, weak access controls, and inadequate monitoring.
3. How do organizations assess AI security risks?
Organizations should evaluate both the likelihood of exploitation and potential business impact, including data sensitivity, financial exposure, operational disruption, regulatory considerations, customer impact, and reputational risk.
4. What are AI security controls?
AI security controls can include identity and access management, least privilege, data protection, encryption, AI guardrails, secure AI development, input validation, output monitoring, API security, human oversight, and third-party risk management.
5. Why is continuous AI risk monitoring important?
AI environments change continuously. Models, data, integrations, permissions, users, vulnerabilities, and attack techniques can change after an initial assessment. Continuous monitoring helps organizations identify when their AI risk profile changes.
IS YOUR ORGANIZATION READY FOR SECURE AI ADOPTION?
Start by mapping your AI environment, identifying your highest-risk exposures, understanding what your AI systems can access, and evaluating whether your current controls are actually reducing risk.
About the Author
Brahma Gupta Illindra
Brahma Gupta is a technology entrepreneur, enterprise technology leader, and Founder & CEO of Indrasol, helping organizations adopt AI, cloud, data, and cybersecurity technologies securely, compliantly, and at scale. Over the years, he has worked across enterprise architecture, data engineering, analytics, cloud technologies, Oracle EPM, and business transformation. Today, his focus is increasingly on one of the biggest challenges facing enterprises: how to adopt AI at scale without losing visibility, security, governance, or control. At Indrasol, he and his team help organizations bridge the gap between technology innovation and business risk across: • AI Security & AI-SPM (AI Security Posture Management) • AI Governance & Responsible AI • Cloud Security & CSPM (Cloud Security Posture Management) • Cybersecurity & Risk Management • SOC 2, ISO 27001, ISO 42001 & CMMC compliance • Cloud modernization & DevOps • Data, analytics & AI transformation • Enterprise technology & automation Brahma is particularly interested in the emerging security challenges created by Generative AI, AI agents, Shadow AI, AI identities, model risk, data exposure, AI governance, and autonomous AI systems. His perspective is simple: AI adoption should create business advantage—not introduce unmanaged risk. He also believes security and compliance should be more than check-the-box exercises. Done correctly, they can help organizations win enterprise customers, accelerate sales cycles, strengthen trust, reduce risk, and scale technology with confidence. Brahma regularly writes about AI security, AI-SPM, cloud security, cybersecurity, AI governance, SOC 2, ISO 27001, ISO 42001, CSPM, enterprise AI adoption, and technology strategy. He enjoys connecting with CISOs, CIOs, CTOs, founders, technology leaders, security professionals, and enterprise teams building the next generation of secure AI and cloud-powered businesses. If you’re working on AI security, cloud security, enterprise AI adoption, cybersecurity, compliance, or digital transformation, connect with Brahma.
View Brahma Gupta Illindra's profile